Palo Alto Patches PAN-OS RCE Flaw Under Active Attack

Palo Alto Networks Patches PAN-OS RCE Vulnerability Amid Active Exploitation
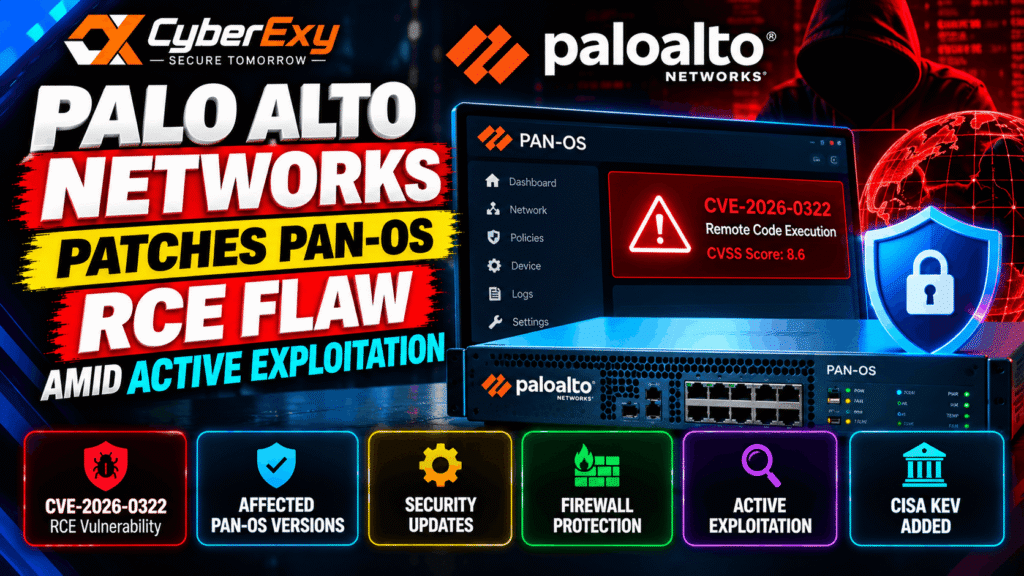
Palo Alto Networks has released security updates for a high-severity remote code execution (RCE) vulnerability in its PAN-OS firewall software. Tracked as CVE-2026-0322, the vulnerability has a reported CVSS score of 8.6 and is being actively exploited, according to the company’s security advisory.
The flaw affects the management interface and could allow an authenticated attacker with network access to execute arbitrary code with root privileges on an affected firewall. Palo Alto Networks has acknowledged limited exploitation attempts and recommends applying the relevant security updates.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has also added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalog, highlighting the need for timely remediation.
What Is CVE-2026-0322?
CVE-2026-0322 is a remote code execution vulnerability affecting the management interface of Palo Alto Networks PAN-OS software.
According to the vendor’s official security advisory, an authenticated attacker with network access to the management interface could exploit the flaw to execute arbitrary code with root privileges.
Root-level access can give an attacker extensive control over a compromised system. In a firewall environment, such access could threaten the security and reliability of a critical network security device.
Although authentication is required, exposure of the management interface to untrusted networks can increase the opportunity for exploitation.
Which Products Are Affected?
According to the supplied disclosure, CVE-2026-0322 affects PAN-OS software running on:
- Palo Alto Networks PA-Series firewalls
- Palo Alto Networks VM-Series firewalls
- Panorama virtual appliances
- Panorama M-Series appliances
Cloud NGFW and Prisma Access are not affected, according to Palo Alto Networks.
Organisations should identify their deployed products and exact PAN-OS versions before deciding which remediation steps to apply.
PAN-OS Security Updates and Fixed Versions
Palo Alto Networks has provided fixed releases across several PAN-OS branches.
The supplied advisory lists the following fixed versions:
| PAN-OS branch | Fixed versions |
|---|---|
| 12.2 | 12.2.4 and later |
| 12.1 | 12.1.4-h12, 12.1.7-h8, 12.1.10-h2 and later listed fixes |
| 11.2 | 11.2.4-h22, 11.2.7-h21, 11.2.10-h15, 11.2.13-h3 and 11.2.16 |
| 11.1 | 11.1.4-h37, 11.1.6-h39, 11.1.7-h11, 11.1.10-h35, 11.1.13-h15 and 11.1.16-h3 |
| 10.2 | 10.2.7-h38, 10.2.10-h41, 10.2.13-h26, 10.2.16-h11 and 10.2.18-h12 |
The source identifies PAN-OS 11.2.16 as having an estimated availability date of October 15, 2026. Administrators should verify the current status of that release and confirm the applicable fixed version in the official Palo Alto Networks advisory before updating.
Do not assume that a version is protected simply because it belongs to the same major release branch. Check the precise maintenance release and hotfix requirements.
Active Exploitation and CISA’s Response
Palo Alto Networks acknowledged seeing very limited exploitation targeting its management interface. The supplied report does not identify the attackers or establish the full scope of the activity.
It lists three IP addresses assessed as being associated with the reported exploit attempts:
66.42.72[.]14208.83.239[.]114149.248.47[.]234
These indicators should be treated as investigation leads rather than conclusive evidence of compromise. Security teams should validate suspicious connections against their own firewall logs and other telemetry before taking action.
CISA added CVE-2026-0322 to its KEV catalog. The supplied report states that Federal Civilian Executive Branch agencies must prioritise remediation by October 17, 2026.
Organisations should consult the CISA Known Exploited Vulnerabilities Catalog for the applicable listing and remediation requirements.
How Organisations Can Reduce the Risk
Security teams should take the following actions:
1. Apply the appropriate security update. Identify affected devices and install a vendor-provided fixed release after following the organisation’s change-management process.
2. Restrict management-interface access. Palo Alto Networks recommends limiting access to trusted internal IP addresses. Where practical, restrict management access to a dedicated, controlled jump host.
3. Review firewall logs. Investigate unusual management-interface connections, authentication activity and unexpected administrative actions.
4. Validate possible compromise. If suspicious activity is detected, preserve relevant logs and follow the organisation’s incident-response procedures. Do not rely on patching alone to establish that a previously exposed device is clean.
5. Maintain an accurate asset inventory. Track firewall models, software branches and installed hotfixes so that urgent vulnerabilities can be assessed quickly.
A Wider Warning for Network Security Devices
The disclosure coincides with reports of active exploitation of a critical Cisco Secure Email Gateway vulnerability, CVE-2026-76519, which has a reported CVSS score of 9.8.
According to the supplied report, the Cisco flaw could allow an unauthenticated remote attacker to write arbitrary files and execute commands with root privileges under affected conditions.
CISA added both vulnerabilities to its KEV catalog. These developments reinforce the importance of monitoring vendor advisories and prioritising vulnerabilities known to be exploited in the wild.
Conclusion
CVE-2026-0322 presents a serious risk to affected PAN-OS deployments because successful exploitation could provide root-level code execution through the firewall management interface. Palo Alto Networks has released fixes and recommends restricting management access to trusted systems.
Administrators should verify affected versions, install the appropriate update and review relevant logs for suspicious activity. Timely patching, restricted administrative access and effective incident response remain essential for protecting network security infrastructure.
CyberExy — Secure Tomorrow.