Fake AI Attacks Target US Companies: How MSSPs Can Respond

Fake AI Attacks Target US Companies: How MSSPs Can Detect and Stop Threats Earlier
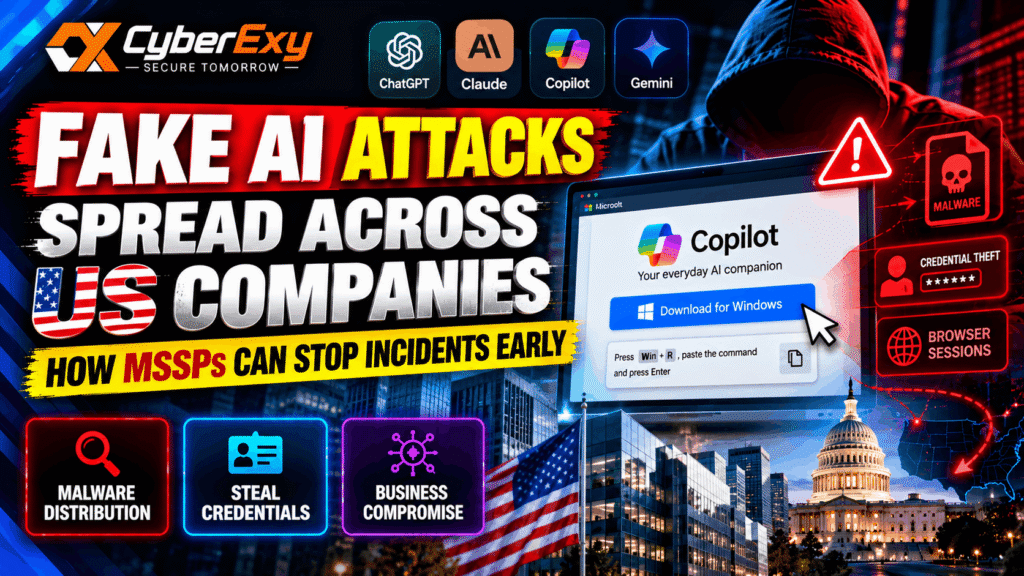
Cybercriminals are exploiting the popularity of artificial intelligence tools to distribute malware, steal credentials and compromise business accounts. By impersonating trusted services such as ChatGPT, Claude, GitHub Copilot and Gemini, attackers can persuade employees to download malicious applications, execute suspicious commands or enter credentials into fraudulent websites.
According to research cited by ANY.RUN, its analysts linked 1,258 public sandbox analyses to fake AI campaigns between April and October 2026. The company’s data also indicated that 16% of country-attributed targets in the observed campaigns were in the United States.
These attacks create a growing operational challenge for managed security service providers (MSSPs), which must protect multiple customers with different systems, security policies and risk profiles. Similar campaigns can trigger repeated investigations, consume analyst time and delay incident response.
For MSSPs, the solution requires more than blocking suspicious domains. Effective protection combines behavioural analysis, threat intelligence, proactive threat hunting and repeatable security operations.
How Fake AI Attacks Are Reaching US Businesses
Fake AI attacks exploit the trust users place in familiar technology brands. Attackers create counterfeit download pages, fraudulent authentication portals and deceptive instructions designed to make malicious activity appear legitimate.
According to ANY.RUN, the campaigns it investigated impersonated services including Claude, ChatGPT, GitHub Copilot and Gemini. Lures appeared through sponsored search results, legitimate hosting platforms, shared AI conversations and counterfeit software websites.
The danger is that users may believe they are installing a legitimate application when they are actually initiating a malicious process. Once execution begins, the attack may use built-in operating-system utilities, making it harder to distinguish malicious activity from ordinary administrative behaviour.

Figure : Fake AI attacks pose a serious risk to business security.
For businesses, this creates a security problem at the intersection of social engineering, software impersonation and endpoint execution. Employee awareness remains important, but organisations also need controls that can detect suspicious behaviour after a user interacts with a fraudulent page.
How a Fake AI Installation Page Can Start an Infection
One campaign described in the source impersonated Claude through a website resembling the official download page. When a visitor selected the Windows download option, the page copied a command to the clipboard and instructed the user to execute it through PowerShell.
Instead of installing the expected application, the command reportedly launched mshta.exe, retrieved a malicious HTML application (HTA) file and initiated an encoded PowerShell execution chain.
This technique uses a familiar user action—installing software—as the starting point for a potentially serious compromise. It also demonstrates why checking a website’s appearance alone is insufficient to establish that a download is safe.

Figure : Fake Copilot installation page.
Although the figure refers to Copilot, the accompanying example in the supplied report describes a Claude impersonation campaign. Keep the caption as supplied if the image itself depicts a counterfeit Copilot page.
Organisations should encourage employees to obtain software through verified vendor websites and approved company portals. Security teams should also investigate unusual command execution associated with application installation.
How Sandbox Analysis Reveals the Full Infection Chain
A suspicious website or file may not reveal its complete behaviour during a simple visual inspection. Some threats only become apparent after a user interacts with the page or the downloaded content executes.
ANY.RUN’s Interactive Sandbox allows analysts to investigate suspicious activity in an isolated environment. Analysts can observe process creation, network connections and subsequent behaviour to understand how a potential infection develops.
The supplied report describes several recurring behaviours associated with the campaigns, including suspicious PowerShell commands, mshta.exe execution, encoded download instructions and scheduled tasks associated with browser-session theft.
These observations help investigators move beyond the initial lure and understand the sequence of events that may have led to a compromise.

Figure : ANY.RUN’s Sandbox revealed the entire infection chain.
For MSSPs, the central benefit of behavioural investigation is consistency. Rather than treating every new domain or fake application as an entirely separate problem, analysts can compare execution patterns, identify recurring behaviours and reuse validated findings across customer environments.
This does not mean every incident can be resolved automatically. Sandbox findings still need to be interpreted in context, and suspected compromises may require endpoint investigation, credential revocation and containment.
Why Fake AI Campaigns Put Pressure on MSSP Operations
ANY.RUN reported that 16% of country-attributed fake AI attacks in its dataset targeted the United States. This is a finding from the company’s observed dataset, not a measure of all cyberattacks against US organisations.

Figure : ANY.RUN data shows that 16% of Fake AI attacks were directed at the US.
For MSSPs, the operational challenge becomes more complex when similar campaigns affect several customers at once. Each customer may use different endpoint tools, cloud platforms, identity systems and incident-response procedures.
Three areas are particularly affected.
1. Detection and Monitoring Coverage
Attackers can rotate domains, change hosting arrangements and impersonate different AI brands. A detection rule that relies exclusively on a previously observed domain may miss a new campaign variant.
MSSPs therefore need to combine indicator-based detection with behavioural analytics. Suspicious process execution, unexpected script interpreters and unusual outbound connections may remain useful investigation signals even when the infrastructure changes.
2. Triage and Escalation Management
Complex execution chains can require more time to investigate than straightforward alerts. If Tier 1 analysts cannot determine whether an event is malicious, cases may be escalated unnecessarily to Tier 2 or Tier 3.
Repeated escalations consume specialist capacity and may delay higher-priority investigations.
3. Threat Hunting and Detection Improvement
A confirmed incident should produce knowledge that can improve future detection. Analysts need a repeatable process for extracting useful indicators, documenting observed behaviours and checking for related activity across other customers.
These activities directly affect operational measures such as mean time to detect (MTTD), mean time to respond (MTTR), escalation rates, investigation costs and service-level agreement (SLA) compliance.
Improving Tier 1 Efficiency Through Behavioural Investigation
One way to improve SOC efficiency is to reduce the time analysts spend establishing whether suspicious activity represents a genuine threat.
A counterfeit AI download page may look convincing, while its malicious behaviour remains hidden until the installation workflow is followed. Static inspection can identify suspicious characteristics, but it may not reveal every subsequent execution stage.
ANY.RUN’s Interactive Sandbox provides a controlled environment for investigating suspicious activity and observing the resulting behaviour.

Figure : ANY.RUN’s Interactive Sandbox detects Fake AI attacks in seconds.
For MSSPs, sandbox analysis can support routine Tier 1 workflows by providing additional evidence for triage decisions. Analysts can use the results to determine whether a case requires containment, deeper investigation or closure.
The source reports a median threat detection time of 14 seconds for the solution. This is a vendor-reported metric and should not be interpreted as a guarantee that every investigation or incident will be resolved within that time.
Turning Investigation Results into Actionable Reports
Consistent reporting helps analysts communicate findings and document the next steps. An actionable report should identify the suspicious activity, explain the supporting evidence, highlight relevant indicators and recommend appropriate investigation or containment actions.

Figure : ANY.RUN generates an actionable Tier 1 report for fast, informed response.
ANY.RUN reports 30% fewer Tier 1-to-Tier 2 escalations when using its sandbox. The actual benefit for an MSSP will depend on its alert volume, analyst experience, integration quality and existing escalation procedures.
The operational objective is not simply to reduce escalations. It is to ensure that routine cases are handled efficiently while serious or ambiguous incidents receive the specialist attention they require.
Expanding Detection Coverage with Threat Intelligence
Sandbox analysis helps investigate suspicious activity that has already attracted attention. Threat intelligence can help MSSPs recognise previously observed malicious infrastructure and connect separate incidents.
This distinction matters because attackers can change individual indicators more easily than they can eliminate every trace of their activity. Domains may change, but related infrastructure, malware characteristics and behavioural patterns can still provide useful investigative leads.
ANY.RUN Threat Intelligence Feeds supply indicators from malware and phishing investigations. These indicators can be incorporated into existing SIEM, EDR and other security workflows, depending on the available integrations.

Figure : ANY.RUN’s TI Feeds offer 99% unique IOCs from the latest malware and phishing.
The source reports that 30% of unique malicious indicators discovered by ANY.RUN customers during sandbox investigations were already available in its TI Feeds. It also claims that its feeds provide 99% unique indicators compared with other threat intelligence sources.
These figures are vendor-reported claims, and their meaning depends on the comparison methodology and dataset. MSSPs should evaluate intelligence sources based on relevance, freshness, accuracy, coverage and compatibility with their existing tools.
The broader principle is that validated intelligence can reduce duplicated investigation work. When one customer experiences a fake AI campaign, analysts can use the resulting indicators and behavioural evidence to search for related activity elsewhere.
Using Threat Intelligence Lookup for Proactive Hunting
Threat hunting extends the value of an investigation beyond the original alert. Instead of waiting for another customer to report a similar incident, analysts can use known indicators and behaviours to search for related activity proactively.
According to the supplied report, ANY.RUN’s Threat Intelligence Lookup helps analysts investigate relationships between suspicious indicators, malware behaviour, historical sightings and associated attacker infrastructure.
For example, after identifying a suspicious domain in one incident, a security team can examine its known relationships and determine whether other customer environments have communicated with related infrastructure.
The team can also translate confirmed findings into detection engineering improvements. Depending on the available telemetry, this may include reviewing endpoint process events, authentication logs, DNS requests, proxy records and other relevant data.
ANY.RUN reports access to 24 times more indicators of compromise per incident through its threat intelligence solutions. MSSPs should independently assess the usefulness of such coverage for their own customer base and detection requirements.
The goal is to turn each investigation into a reusable improvement rather than repeatedly solving the same problem from scratch.
A Practical Response Framework for MSSPs
MSSPs can apply the following workflow to improve their response to fake AI campaigns.
- Validate the initial alert. Establish whether the event involves a suspicious download, fraudulent login page, unusual script execution or another relevant indicator.
- Investigate in an isolated environment. Use approved sandboxing and analysis procedures to examine suspicious files or URLs safely.
- Build an evidence-based timeline. Record process activity, network connections, relevant file changes and observed execution behaviour.
- Contain confirmed incidents. Follow the customer’s incident-response procedures, which may include isolating affected endpoints, revoking exposed sessions and rotating compromised credentials.
- Search across customers where authorised. Use validated indicators and behavioural patterns to identify potentially related activity in other managed environments.
- Improve detections and documentation. Update monitoring rules, playbooks and analyst guidance based on confirmed findings.
- Measure operational results. Track MTTD, MTTR, escalation quality, false positives and SLA performance to determine whether the changes improve outcomes.
This approach combines technical detection with consistent service delivery. It also helps prevent automation from becoming a substitute for sound investigation and human judgement.
How ANY.RUN Supports MSSP Detection and Response
The source describes ANY.RUN’s Interactive Sandbox and Threat Intelligence capabilities as complementary components of an MSSP workflow.
Sandbox analysis supports behavioural investigation and triage. Threat intelligence helps analysts identify related infrastructure, enrich indicators and extend investigations across customer environments.
ANY.RUN reports several performance improvements, including a 36% higher detection rate, up to 58% more threats identified, responses that are 21 minutes faster and 30% fewer Tier 1-to-Tier 2 escalations. These are vendor-reported results rather than independently established outcomes for every MSSP.
For service providers evaluating security tools, the most relevant question is whether the solution improves measurable results in their own environment. A structured pilot can compare investigation times, detection quality, escalation accuracy and analyst workload before and after deployment.
Technology should support a defined operational process, with clear permissions, documented procedures and human review for high-impact decisions.
Conclusion
Fake AI campaigns demonstrate how attackers can exploit familiar software brands and routine employee behaviour to distribute malware, steal credentials and compromise business accounts. The problem is particularly challenging for MSSPs because similar campaigns can affect multiple customers while consuming valuable analyst capacity.
A stronger response combines behavioural investigation, validated threat intelligence, proactive hunting and consistent incident-response procedures. Sandbox analysis can reveal suspicious execution chains, while threat intelligence can help connect related activity and improve detection coverage.
For MSSPs, success means more than detecting a single fake AI campaign. It means turning investigation results into repeatable improvements across the customer base while preserving response quality and service-level commitments.
CyberExy — Secure Tomorrow.