CISA ScubaGear and ScubaGoggles: Free Cloud Security Tools

CISA Offers Two Free Tools to Detect Microsoft 365 and Google Workspace Security Misconfigurations
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) provides two free tools to help organisations identify security misconfigurations in Microsoft 365 and Google Workspace. ScubaGear and ScubaGoggles assess cloud environments against recommended security baselines, helping administrators identify settings that may require attention.
Both tools are part of CISA’s Secure Cloud Business Applications (SCuBA) project, established in 2022 to improve cloud security and visibility. Although the initiative primarily supports U.S. federal civilian agencies, its guidance and tools can also help private organisations strengthen their cloud security practices.
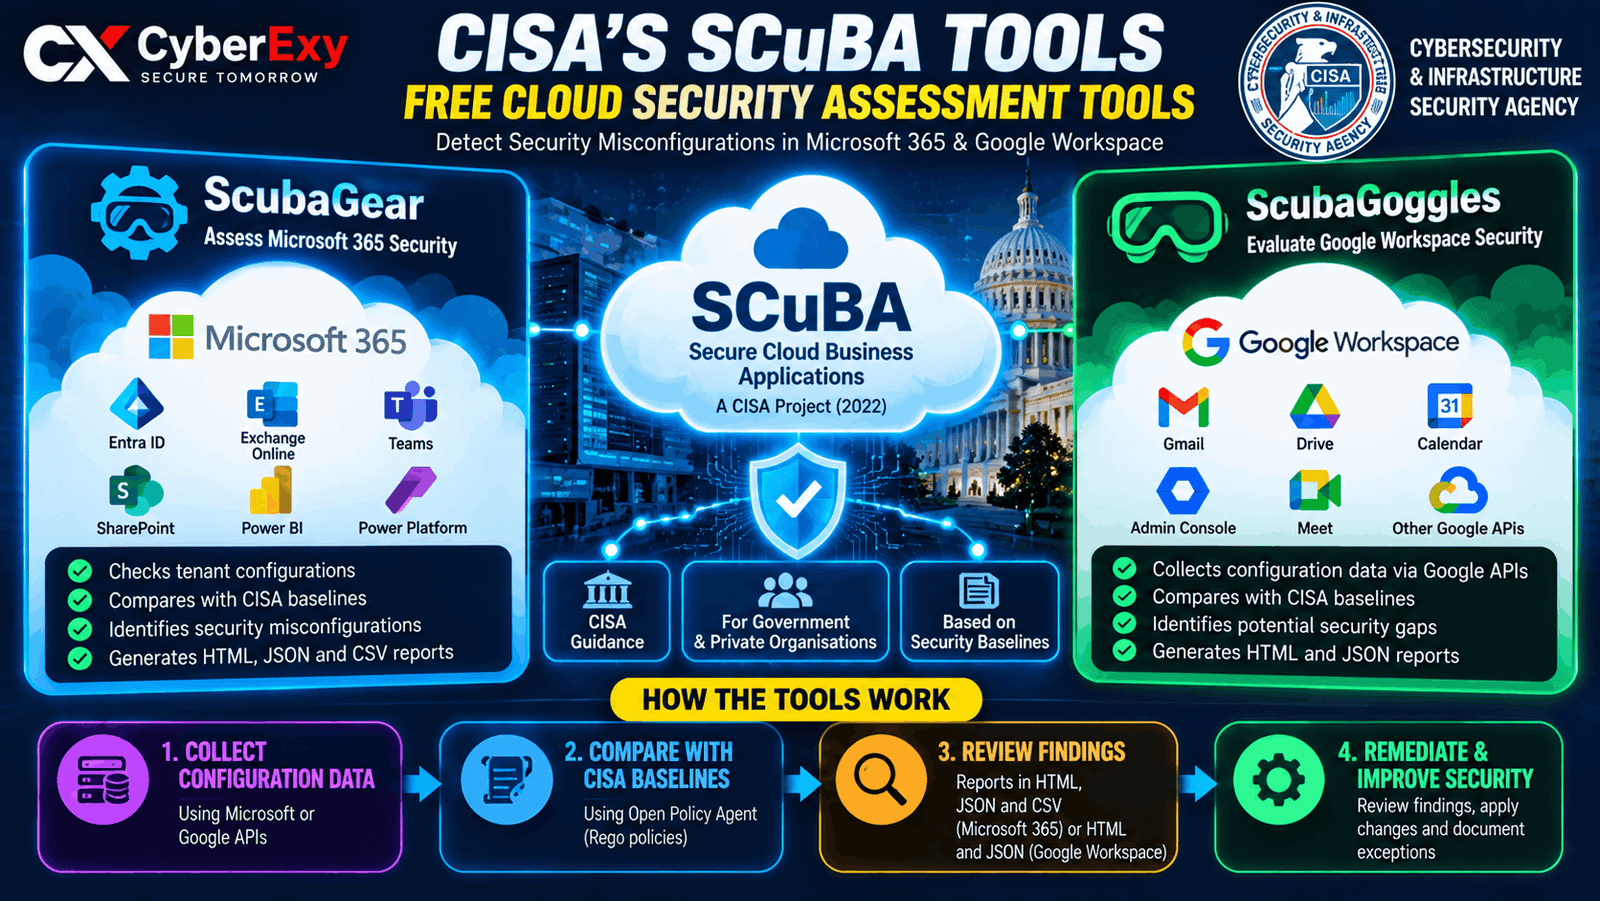
ScubaGear Assesses Microsoft 365 Security
ScubaGear evaluates Microsoft 365 tenant configurations against CISA’s secure configuration baselines. Its coverage includes Microsoft Entra ID, Exchange Online, Microsoft Teams, SharePoint, Power BI, and Power Platform.
The tool uses PowerShell to collect configuration information through Microsoft APIs. It then applies Open Policy Agent (OPA) policies, written in Rego, to compare the collected settings against defined security requirements. The resulting reports are available in HTML, JSON, and CSV formats, making it easier for administrators to review findings and plan remediation.
ScubaGear can help security teams identify configuration gaps involving identity management, collaboration, and other cloud services. Administrators should review the official documentation for current installation requirements, permissions, and dependencies before running an assessment.
Importantly, ScubaGear identifies potential gaps; it does not automatically resolve every finding. Administrators must evaluate the results, apply appropriate changes, and document justified exceptions.
Official project: https://github.com/cisagov/ScubaGear
ScubaGoggles Reviews Google Workspace Configurations
ScubaGoggles performs a similar role for Google Workspace. It collects relevant configuration information using the Google Admin SDK and other Google APIs, then evaluates the collected data against CISA’s security baselines using policy-based checks.
Its reports help administrators examine settings across Google Workspace services and identify areas that may need further investigation. This can support security reviews involving user privileges, organisational settings, and cloud collaboration services.
However, CISA’s repository warns that ScubaGoggles is under active development and that assessment results may be incorrect. Administrators should validate findings, investigate unexpected results, and complete any required manual checks before making security decisions.
Official project: https://github.com/cisagov/ScubaGoggles
Why Cloud Security Baselines Matter
Cloud misconfigurations can expose sensitive information, weaken authentication controls, or grant users more access than necessary. Regular configuration assessments help organisations detect deviations from recommended security practices before those weaknesses contribute to an incident.
Security teams can use these tools to establish a baseline, review findings, prioritise remediation, and repeat assessments after significant configuration changes. They should also maintain records of accepted risks and exceptions where business requirements prevent immediate remediation.
Neither tool guarantees that a cloud environment is secure. Baseline assessments should complement identity protection, access reviews, logging, monitoring, incident response, and other security controls.
Conclusion
CISA’s ScubaGear and ScubaGoggles offer practical ways to evaluate Microsoft 365 and Google Workspace configurations against established security baselines. By reviewing results carefully and addressing relevant findings, organisations can improve cloud security visibility and build a more consistent configuration-management process.
For administrators responsible for cloud environments, these tools provide a useful starting point for identifying potential weaknesses and improving security hygiene.
Source: CISA SCuBA project and the official ScubaGear and ScubaGoggles repositories.
Disclaimer: This article is for educational and informational purposes. Always follow official documentation and organisational change-management procedures when assessing production cloud environments.