Ransomware Groups Exploit Palo Alto GlobalProtect Flaw for Stealthy VPN Access

Introduction
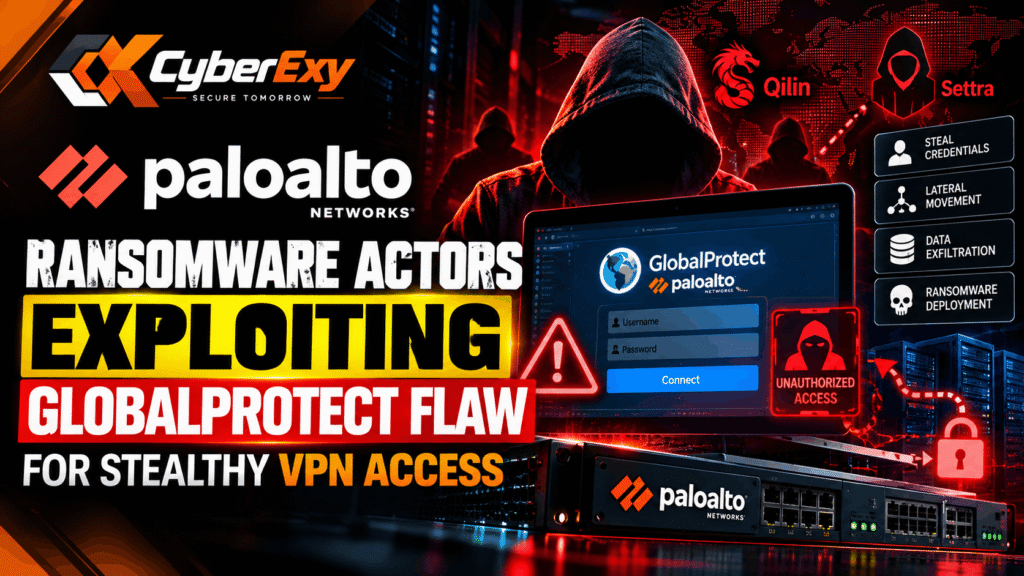
Ransomware groups are reportedly exploiting a vulnerability in Palo Alto Networks GlobalProtect to gain unauthorized access to corporate networks through trusted virtual private network (VPN) connections. According to ReliaQuest, threat groups including Qilin and Settra are abusing CVE-2026-0257, an authentication bypass affecting certain PAN-OS GlobalProtect and Prisma Access configurations.
The activity presents a significant cybersecurity concern because attackers can enter internal networks through legitimate remote-access infrastructure. Their connections may resemble normal employee activity, making detection more difficult for security teams.
Understanding CVE-2026-0257
CVE-2026-0257 is an authentication bypass vulnerability associated with specific GlobalProtect configurations. Palo Alto Networks disclosed the issue on 13 May 2026, assigning it a CVSS score of 7.8 and a High severity rating.
The vulnerability involves authentication override cookies used by GlobalProtect portals and gateways. Under certain configuration conditions, insufficient validation and integrity protections can allow an unauthenticated attacker to bypass security restrictions and establish an unauthorized VPN session.
However, not every Palo Alto Networks deployment is vulnerable. Exposure depends on the configuration of authentication override cookies and the relevant certificate settings.
Affected software includes releases within the PAN-OS 12.1, 11.2, 11.1 and 10.2 branches, alongside specified Prisma Access releases. Administrators should consult the official Palo Alto Networks security advisory to identify affected builds and the appropriate fixed versions.
How Ransomware Groups Abuse VPN Access
According to ReliaQuest, Qilin and Settra have been associated with exploitation of CVE-2026-0257. Once attackers obtain unauthorized VPN access, they may attempt to expand their foothold inside the target network.
Potential post-compromise activities include:
- Credential theft: Obtaining authentication information to access additional accounts and systems.
- Lateral movement: Exploring internal networks and reaching other devices or servers.
- Reconnaissance: Using tools such as BloodHound and SharpHound to map Active Directory relationships and permissions.
- Command-and-control activity: Using frameworks such as Cobalt Strike to support further operations.
- Data theft and ransomware preparation: Collecting sensitive information and preparing systems for disruptive attacks.
These tools can also be used in legitimate security testing, so their presence alone does not prove malicious activity. Security teams should investigate the surrounding behaviour, account activity, network connections and execution history.
Why the Vulnerability Is Difficult to Detect
VPN connections are commonly trusted because employees and contractors rely on them to access internal resources. An attacker using a compromised or unauthorized VPN session may therefore generate traffic that appears similar to legitimate remote work.
This creates a challenge for traditional perimeter security. Monitoring only whether a VPN connection succeeds may not reveal suspicious activity occurring afterwards.
Organisations should correlate VPN authentication records with endpoint detection alerts, identity-provider logs, directory-service activity and unusual access to sensitive resources. Unexpected devices, unfamiliar connection patterns and abnormal administrative activity deserve additional investigation.
How to Protect GlobalProtect Deployments
Organisations using potentially affected GlobalProtect or Prisma Access configurations should prioritise the following measures:
- Install security updates: Identify affected releases and upgrade to the fixed versions specified in the official vendor advisory.
- Review authentication override cookies: Disable this feature where it is not required and follow the vendor’s recommendations for dedicated certificates.
- Terminate existing VPN sessions: After patching, follow vendor guidance to invalidate potentially affected sessions and require users to authenticate again.
- Investigate suspicious activity: Review VPN logs, unexpected hostnames, authentication anomalies and evidence of lateral movement.
- Strengthen monitoring: Correlate VPN, endpoint and identity logs to detect activity that continues after initial access.
- Check all gateways: Verify that relevant internal and external portals, gateways and hybrid deployments have been remediated consistently.
Patching is essential, but it should not replace an investigation into possible earlier exploitation. Attackers may have established access before the vulnerability was fixed.
Conclusion
The reported exploitation of CVE-2026-0257 highlights the risks associated with vulnerabilities in trusted remote-access infrastructure. Ransomware groups can use unauthorized VPN access as an entry point for credential theft, internal reconnaissance and further malicious activity.
Organisations should verify their exposure, apply vendor-recommended updates, review existing sessions and investigate suspicious post-authentication behaviour. Combining timely patching with continuous monitoring and strong access controls can help reduce the risk of ransomware incidents involving GlobalProtect.
Security takeaway: Treat unexpected VPN activity as a potential early warning sign, even when connections originate through trusted remote-access services.