Hackers Exploit SiteGuard WAF Vulnerability (CVE-2026-106931)

Hackers Exploit SiteGuard WAF Vulnerability That Could Give Them Full Control of Servers
Published: October 2026 | CyberExy — Secure Tomorrow
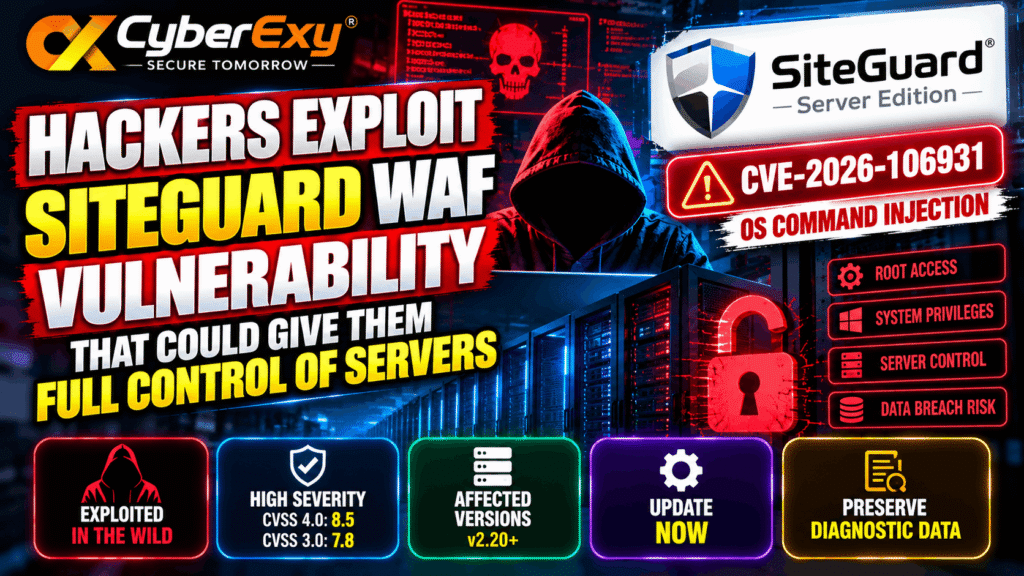
A critical security vulnerability in SiteGuard Server Edition, a host-based web application firewall (WAF), is being exploited in the wild. Tracked as CVE-2026-106931, the flaw could allow an attacker to execute operating system commands with root or SYSTEM privileges on an affected server.
The vulnerability affects the product’s statistics-processing function, which is enabled by default. According to EG Secure Solutions, the company behind SiteGuard, exploitation has already been confirmed. Japan’s vulnerability coordination service, JVN, published an advisory on October 14, 2026, and JPCERT/CC also issued a security alert.
Administrators using affected versions should check their installations, preserve diagnostic information and apply the appropriate update or vendor-provided patch.
What Is the SiteGuard WAF Vulnerability CVE-2026-106931?
CVE-2026-106931 is an operating system command injection vulnerability classified as CWE-78. It affects the statistics feature of SiteGuard Server Edition, a security product integrated directly into web servers.
Command injection occurs when an application handles input in a way that allows unintended operating system commands to be executed. Depending on the application’s permissions and configuration, successful exploitation can have serious consequences.
In this case, an attacker who meets the required access conditions may be able to execute arbitrary commands with elevated privileges on the affected system.
The published severity ratings are:
- CVSS 4.0: 8.5 – High
- CVSS 3.0: 7.8 – High
Although the potential impact is severe, the published vulnerability metrics specify a local attack vector and low privileges required. Therefore, this should not be described as a confirmed login-free remote attack.
The vendor and Japanese security authorities have confirmed exploitation, but the available advisories do not identify the attackers, affected organizations or total number of incidents.
How the Vulnerability Could Affect Servers
SiteGuard Server Edition operates as a host-based WAF, meaning it is integrated into the web server it protects. The vulnerable statistics function introduces a potential path to operating system command execution.
If an attacker successfully exploits the flaw, the consequences could include:
- Unauthorized system access: Commands may execute with root or SYSTEM privileges.
- Confidentiality risks: Sensitive files and information could become accessible.
- System integrity compromise: An attacker may be able to modify files or system settings.
- Service disruption: Unauthorized changes could affect the availability of the server or hosted applications.
- Incident investigation challenges: Applying an update or patch may remove traces that would otherwise help investigators understand an attack.
These are potential consequences of successful exploitation, not confirmation that every affected installation has been compromised.
Which SiteGuard Server Edition Versions Are Affected?
According to the official JVN advisory, the vulnerability affects SiteGuard Server Edition version 2.20 and later when the statistics feature is enabled.
| Product edition | Affected versions | Fixed version |
|---|---|---|
| Apache httpd, Nginx and IIS editions, excluding FreeBSD | Versions before 8.00 Update 5, subject to the affected-version conditions | 8.00 Update 5 |
| Apache httpd and Nginx on FreeBSD | Versions before 7.00 Update 6, subject to the affected-version conditions | 7.00 Update 6 |
| IIS edition, versions 3.10 through 4.00 Update 4 | Not affected by this vulnerability | No update required specifically for this flaw |
Important: The vulnerability affects installations where the statistics feature is enabled, and this feature is enabled by default. Administrators should verify both their product version and configuration.
Consult the vendor’s current advisory before deciding whether an installation requires remediation.
How to Protect SiteGuard Installations
EG Secure Solutions provides two remediation options: updating to a fixed version or applying a vendor-provided patch where upgrading is not possible.
1. Identify affected installations
Determine which servers run SiteGuard Server Edition and record the installed product version, operating system and web-server edition.
Check whether the statistics feature is enabled. Because it is enabled by default, do not assume that an installation is unaffected simply because the feature was never deliberately configured.
2. Preserve diagnostic information
Before applying an update or patch, download and securely retain the product’s diagnostic information.
The vendor warns that remediation may erase traces of an attack. Preserving this information first can help security teams investigate possible unauthorized activity.
The documented interface path is:
Web management interface → Diagnostic Information → Download Diagnostic Information
Store the downloaded file securely and restrict access to authorized personnel.
3. Install the appropriate update
Upgrade to the fixed release applicable to your installation:
- Apache httpd, Nginx and IIS editions outside FreeBSD: Version 8.00 Update 5
- FreeBSD Apache httpd and Nginx editions: Version 7.00 Update 6
Follow the vendor’s official instructions and validate the installation after remediation.
4. Apply the vendor patch if an upgrade is not possible
For organizations unable to upgrade, EG Secure Solutions provides a patch that replaces files used for statistics processing. The vendor states that this option is also available for end-of-life versions.
Obtain the patch and instructions through the official vendor support channel. Do not replace application files using unofficial downloads or unverified instructions.
5. Investigate possible compromise
Because exploitation has been confirmed, affected organizations should assess whether their systems show signs of unauthorized activity.
Security teams should review available logs and diagnostic data, investigate unexpected privileged activity and follow the vendor’s guidance. If compromise is suspected, involve the organization’s incident-response team and preserve relevant evidence.
Why This Vulnerability Matters for Web Security
A WAF is intended to help protect web applications against malicious requests and other attacks. However, the security product itself must also be maintained and monitored.
CVE-2026-106931 illustrates an important principle: defensive software can introduce its own security risks when a component contains a vulnerability. Organizations should therefore include WAFs, endpoint security products, management interfaces and other security tools in their normal vulnerability-management programme.
Useful preventive measures include maintaining a current inventory of security products, reviewing vendor advisories, applying updates promptly and ensuring that access to administrative functions is appropriately restricted.
Organizations should also maintain reliable backups, centralize security logging where practical and establish incident-response procedures before an emergency occurs.
Conclusion
The SiteGuard Server Edition vulnerability CVE-2026-106931 presents a serious risk because successful exploitation could allow operating system commands to run with root or SYSTEM privileges. The vulnerability affects the statistics function, which is enabled by default, and exploitation has been confirmed by the vendor.
Administrators should identify affected versions, preserve diagnostic information before remediation and install the appropriate fixed release or vendor patch. They should also investigate potential signs of compromise rather than assuming that applying a security update automatically resolves every incident.
The key takeaway: Security products require the same disciplined patch management, access controls and monitoring as the systems they are designed to protect.
Follow CyberExy — Secure Tomorrow for cybersecurity news, vulnerability updates and practical defensive security guidance.
Official Sources and Further Reading
- JVN — SiteGuard Server Edition Vulnerable to OS Command Injection: https://jvn.jp/en/jp/JVN88474777/
- EG Secure Solutions — Official Security Advisory: https://www.eg-secure.co.jp/siteguard/news/alert-202610-1
- JPCERT/CC — Security Alert: https://www.jpcert.or.jp/at/2026/at260032.html
- Tenable — CVE-2026-106931 Details: https://www.tenable.com/cve/CVE-2026-106931
Security information is based on advisories published in October 2026. Check the official vendor advisory for the latest remediation guidance and product-specific requirements.