Google Fixes 10 Chrome Vulnerabilities, Including Claude AI Bug Copy title

Google Fixes 10 Chrome Vulnerabilities, Including Memory Corruption Bug Found With Claude AI
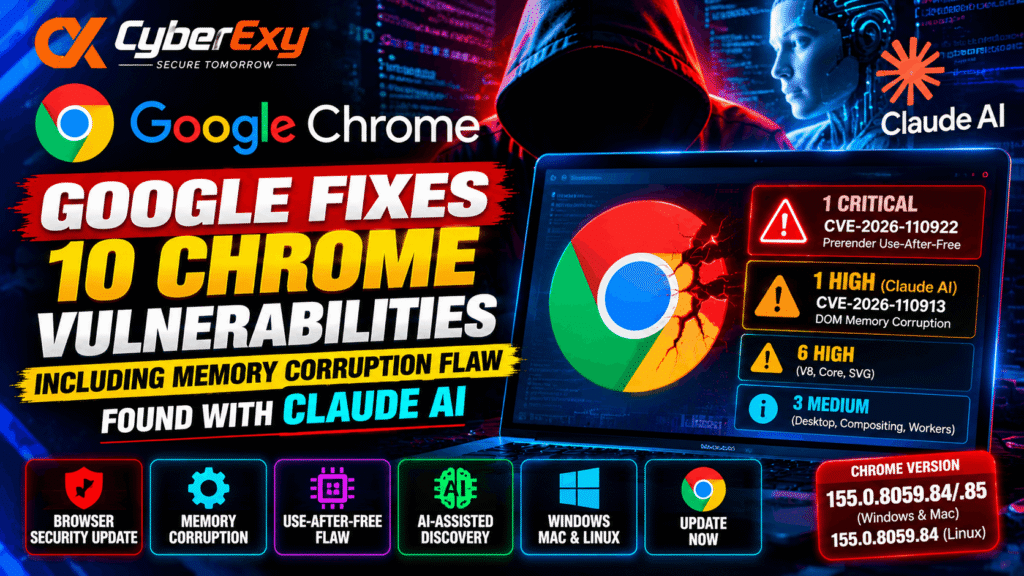
Google has released a Chrome Stable security update addressing 10 vulnerabilities affecting Windows, macOS and Linux. The October 15, 2026, release includes a critical use-after-free vulnerability in Chrome’s Prerender feature and a high-severity memory corruption flaw in the Document Object Model (DOM) that was reported with assistance from Anthropic’s Claude AI.
The update addresses one critical, six high-severity and three medium-severity vulnerabilities across several browser components, including Prerender, DOM, V8, Core, SVG, Desktop, Compositing and Workers.
Google is gradually rolling out Chrome versions 155.0.8059.84/.85 for Windows and macOS, and 155.0.8059.84 for Linux. Users should update their browsers as soon as the fixed version becomes available.
The release also highlights the growing role of AI-assisted research in software security. However, Google’s published information does not establish precisely how Claude contributed to discovering the DOM vulnerability.
Google Releases Chrome Security Update for 10 Vulnerabilities
Chrome is a widely used browser, making security flaws in its components important for individual users, businesses and organisations managing large numbers of endpoints.
According to the supplied report, Google’s October 15 update addresses 10 security issues with varying severity levels. The vulnerabilities affect different parts of the browser, demonstrating why security updates need to cover more than one subsystem.
The most serious issue is CVE-2026-110922, a critical use-after-free vulnerability in the Prerender feature. The update also addresses CVE-2026-110913, a high-severity memory corruption flaw in Chrome’s DOM that Xinyang Ge of Anthropic reported with Claude’s assistance.
Google has not stated that either vulnerability is being actively exploited. Users should therefore distinguish the severity of a reported vulnerability from confirmed evidence of attacks in the wild.
Critical Chrome Vulnerability CVE-2026-110922
The most severe issue listed in the supplied report is CVE-2026-110922, a critical use-after-free vulnerability affecting Chrome’s Prerender feature.
A use-after-free vulnerability occurs when software attempts to access memory after that memory has been released. Depending on the circumstances, this type of programming error can cause a crash, memory corruption or potentially more serious security consequences.
Chrome’s Prerender feature prepares certain pages before a user opens them to improve browsing performance. A vulnerability in this area can therefore raise security concerns because it involves browser functionality that processes web content.
Google credits Xinyang Ge with reporting the issue on October 2, 2026. The company has not published further technical details in the supplied release information, and it has not confirmed active exploitation.
Users should install the appropriate Chrome update rather than wait for additional technical details to become public.
Claude AI Assisted Discovery of a Chrome DOM Memory Corruption Flaw
Another significant issue is CVE-2026-110913, a high-severity memory corruption vulnerability in Chrome’s Document Object Model.
The DOM represents the structure of a web page and allows browser components and scripts to interact with elements such as text, images, forms and other page content. Memory corruption in this area can undermine browser stability and may create security risks depending on the underlying defect.
According to the supplied report, Xinyang Ge reported the vulnerability on September 29 with assistance from Anthropic’s Claude AI. Google publicly credited that assistance in its release information.
However, the available description does not explain whether Claude identified the original defect, helped analyse a suspected issue, or contributed during another stage of the research process. It would therefore be inaccurate to claim that Claude independently discovered or exploited the vulnerability.
The finding nevertheless illustrates a potential role for AI in security research: assisting human researchers with vulnerability analysis and software investigation. The reported case does not establish that AI alone performed the complete discovery process.
Full List of Chrome Vulnerabilities Fixed
The supplied article identifies the following 10 vulnerabilities and affected components.
| CVE ID | Severity | Affected component | Reported by |
|---|---|---|---|
| CVE-2026-110922 | Critical | Prerender | Xinyang Ge |
| CVE-2026-110913 | High | DOM | Xinyang Ge, Anthropic, with Claude assistance |
| CVE-2026-110919 | High | V8 | Xinyang Ge |
| CVE-2026-110918 | High | Core | |
| CVE-2026-110917 | High | SVG | C0rk1 |
| CVE-2026-110921 | High | V8 | Xinyang Ge |
| CVE-2026-110920 | High | V8 | Xinyang Ge |
| CVE-2026-110916 | Medium | Desktop | |
| CVE-2026-110915 | Medium | Compositing | |
| CVE-2026-110914 | Medium | Workers |
The vulnerabilities affect separate browser components, including the V8 JavaScript engine, which executes JavaScript used by modern websites.
The report identifies additional use-after-free and memory corruption issues in V8, Core and SVG. It also lists medium-severity issues involving input validation in Desktop, use-after-free in Compositing and memory corruption in Workers.
Google may restrict access to detailed vulnerability information until a sufficient number of users have installed the fixes. This can help reduce the opportunity for attackers to use newly disclosed technical details against systems that remain unpatched.
How to Update Google Chrome
Chrome updates are distributed gradually, so the fixed version may not appear on every device at the same time.
Windows, macOS and Linux users can check for the update through Chrome’s built-in update interface.
- Open Google Chrome.
- Select the three-dot menu in the upper-right corner.
- Open Help, then select About Google Chrome.
- Allow Chrome to check for available updates.
- Install the update if offered.
- Select Relaunch when prompted to complete the installation.
After restarting, revisit the About Google Chrome page and confirm the installed version.
The supplied report lists versions 155.0.8059.84/.85 for Windows and macOS, and 155.0.8059.84 for Linux. Because rollout timing and platform-specific builds can vary, users should verify the appropriate fixed release through Google’s official Chrome release information.
Guidance for Enterprise Administrators
Organisations managing Chrome across multiple devices should follow their normal browser patch-management process.
IT teams should inventory managed Chrome installations, prioritise devices that have not received the fixed release and confirm deployment through endpoint-management tools. They should also investigate devices where updates repeatedly fail or browser restarts remain pending.
Centralised update monitoring can help organisations identify vulnerable endpoints before they become overlooked exceptions in an otherwise well-maintained environment.
Google’s Approach to Finding Memory Safety Bugs
The supplied report states that Google uses tools including AddressSanitizer, MemorySanitizer, libFuzzer and AFL to identify security problems during software development.
These tools support different aspects of software testing. Sanitizers can help detect memory errors during execution, while fuzzing tools supply varied or malformed inputs to uncover unexpected program behaviour.
Automated testing is valuable because modern browsers contain many interacting components and process complex web content. However, no single tool can identify every vulnerability.
The reported Claude-assisted DOM finding adds another dimension to this approach: AI assistance may support human researchers during code analysis and investigation. The exact contribution in this case remains unspecified in the supplied report.
Combining automated testing, human-led security research, responsible disclosure and timely patch distribution remains important for browser security.
Why Chrome Users Should Install Security Updates Promptly
Browser vulnerabilities deserve attention because browsers process content from many different websites and services. A vulnerable component may be exposed during ordinary browsing, although the actual risk depends on the nature of the flaw and the conditions required to trigger it.
This update includes a critical issue and several high-severity vulnerabilities. Even without confirmation of active exploitation, installing the fixed version reduces exposure to the known defects addressed by the release.
Users should avoid postponing updates unnecessarily, while organisations should ensure that managed endpoints receive patches according to their security policies.
For additional information, consult Google’s Chrome Releases blog and the Chrome security information page.
Conclusion
Google’s October 15, 2026, Chrome Stable update fixes 10 vulnerabilities across Windows, macOS and Linux. The release includes the critical Prerender use-after-free issue CVE-2026-110922 and the high-severity DOM memory corruption flaw CVE-2026-110913, which was reported with assistance from Claude AI.
The case highlights the potential value of AI-assisted vulnerability research while underscoring the importance of precise attribution. Google has not publicly detailed Claude’s exact role or confirmed that these vulnerabilities are being actively exploited.
Users should check for the fixed Chrome release, install available updates and restart their browsers. Enterprise administrators should verify deployment across managed endpoints and investigate devices that remain unpatched.
CyberExy — Secure Tomorrow.