Top 10 Mobile Application Security Testing Tools in 2026

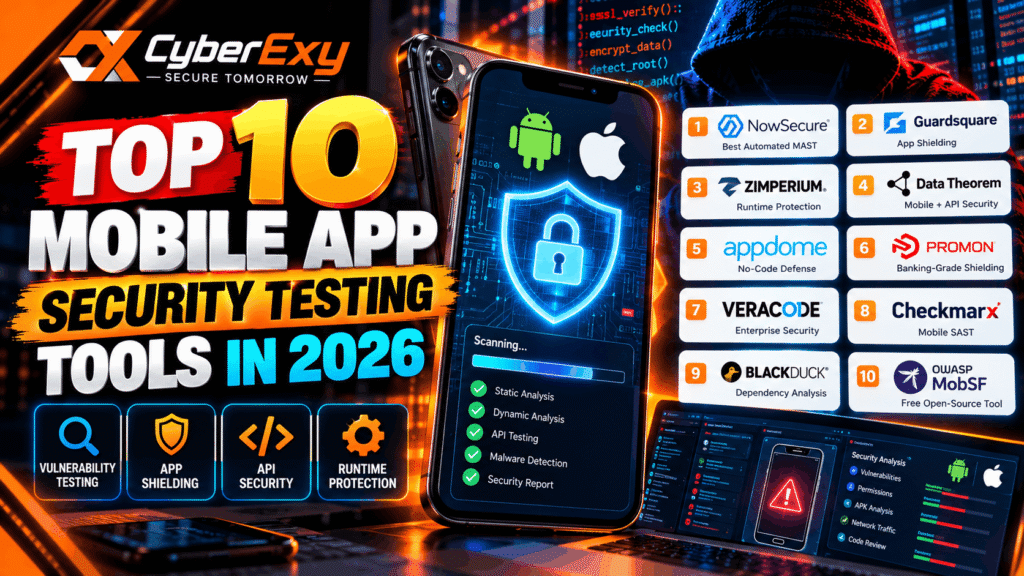
Top 10 Best Mobile Application Security Testing Tools in 2026
1. Introduction
Mobile applications have become essential to banking, e-commerce, healthcare, communication and business operations. They frequently process sensitive information, including personal details, authentication tokens, payment data and confidential business records. As a result, vulnerabilities in mobile applications can create significant security and privacy risks.
Mobile application security testing helps developers and security professionals identify weaknesses before applications are released and throughout their lifecycle. However, protecting a mobile application requires more than checking its source code. Applications also interact with backend APIs, rely on third-party libraries and execute on devices that may be compromised or controlled by attackers.
This is why organisations increasingly combine mobile application security testing (MAST) with application shielding, runtime protection and dependency analysis.
This guide reviews ten mobile security tools identified in the supplied 2026 research. It explains their capabilities, strengths, limitations and potential use cases to help development teams, cybersecurity professionals and businesses choose an appropriate security strategy.
The rankings and scores below are editorial assessments from the supplied source, not results from independent laboratory testing.
2. What Is Mobile Application Security Testing?
Mobile application security testing is the process of examining Android and iOS applications to identify weaknesses that could expose information, compromise user accounts or allow unauthorised actions.
A comprehensive testing programme can include several complementary techniques.
Static Application Security Testing (SAST)
SAST examines application source code or compiled packages to identify potentially insecure coding patterns. Depending on the tool, it can help detect hard-coded secrets, insecure data handling, weak cryptographic practices and other coding risks.
Static analysis is useful during development because teams can investigate findings before releasing an application.
Dynamic Application Security Testing (DAST)
Dynamic testing examines an application while it is running. It can help identify problems involving authentication, network communication, session management and runtime behaviour.
Testing in a controlled environment can reveal weaknesses that are difficult to understand through source-code inspection alone.
API Security Testing
Mobile applications often rely on backend APIs to retrieve information, authenticate users and process transactions. API security testing helps identify issues such as broken access controls, excessive data exposure and inadequate authentication.
Testing both the mobile client and its backend services provides a more complete view of the application’s security.
Software Composition Analysis (SCA)
SCA identifies third-party libraries and open-source components used by an application. It helps teams assess dependency vulnerabilities and software licence obligations.
This is important because a mobile application may inherit security risks from components developed and maintained by other organisations.
Runtime Application Self-Protection (RASP)
RASP technologies monitor application behaviour during execution and may detect or respond to selected threats. Depending on the implementation, they can help identify suspicious instrumentation, tampering or compromised execution environments.
Application Shielding
Application shielding makes certain attacks against a deployed application more difficult. Techniques may include code obfuscation, anti-tampering and anti-hooking protections.
Shielding complements vulnerability testing but does not eliminate underlying software vulnerabilities.
3. Why Mobile App Security Matters in 2026
Mobile security risks extend beyond the application package itself. Developers must consider the entire environment in which the application operates.
Important risk areas include:
- Sensitive data exposure: Personal information, authentication tokens or confidential records may be stored or transmitted insecurely.
- Weak authentication: Inadequate authentication and session controls can allow unauthorised access.
- Insecure APIs: Backend services may expose data or functionality without sufficient access-control checks.
- Vulnerable dependencies: Third-party libraries can introduce security weaknesses.
- Reverse engineering: Attackers may inspect application binaries to understand business logic or identify sensitive information.
- Runtime manipulation: Compromised devices and instrumentation tools can be used to inspect or alter application behaviour.
- Inadequate monitoring: Security weaknesses may remain undetected when applications are not tested regularly.
A structured mobile application security programme combines preventive development practices, regular testing and appropriate protection for deployed applications.
4. How We Evaluated the Tools
The supplied research evaluates the tools using five criteria.
| Criterion | Weight |
|---|---|
| Depth within the tool’s primary security area | 30% |
| Standards alignment | 25% |
| CI/CD integration and developer experience | 20% |
| Pricing transparency | 15% |
| Ecosystem and integration capabilities | 10% |
The methodology considers testing capabilities, standards alignment, application shielding, runtime protection, development workflow integration and pricing information.
The original research states that the assessment is research-based and does not include laboratory testing. The scores should therefore be interpreted as editorial comparisons rather than independently measured performance results.
Another important consideration is that these products do not all perform the same function. A source-code analysis platform, an application-shielding product and a dynamic testing framework address different parts of the mobile security lifecycle.
5. Top 10 Mobile Application Security Testing Tools in 2026
1. NowSecure – Best for Automated Mobile Application Security Testing
NowSecure ranks first in the supplied comparison because of its focus on dedicated mobile application security testing, standards mapping and development pipeline integration.
The research highlights static, dynamic, interactive and API assessments. It also identifies physical-device testing and integration with continuous integration and continuous delivery (CI/CD) pipelines as important capabilities.
For development teams, automated testing can help incorporate security checks into regular development activities instead of relying entirely on a final pre-release assessment.

Key features
- Automated mobile application security testing.
- Static, dynamic, interactive and API assessments.
- Mapping to OWASP MASVS-related requirements.
- CI/CD pipeline integration.
- Security reporting for development and assessment workflows.
Advantages
NowSecure focuses specifically on mobile security testing. Its standards-oriented approach can help teams connect technical findings to defined security requirements.
Automation can also support more consistent testing across successive application builds.
Limitations
The supplied research positions NowSecure primarily as a testing solution rather than a complete application-shielding platform. Organisations requiring extensive runtime protection may need complementary products.
Best use case: Development teams that want repeatable mobile security assessments integrated into their software delivery process.
2. Guardsquare – Best for Application Shielding and Initial Free Scanning
Guardsquare specialises in protecting mobile applications against reverse engineering, tampering and selected forms of runtime manipulation.
Its product portfolio includes DexGuard for Android and iXGuard for iOS. The supplied research also identifies AppSweep as a free mobile vulnerability scanning option.
Code obfuscation makes application logic more difficult to understand, while anti-tampering protections can help detect or resist modifications to an application.
These capabilities are particularly relevant when an organisation distributes an application to devices outside its direct control.

Key features
- Android and iOS application shielding.
- Code obfuscation.
- Anti-tampering protections.
- Defences against selected dynamic instrumentation techniques.
- AppSweep vulnerability scanning.
Advantages
Guardsquare combines specialised application protection with an accessible starting point for vulnerability scanning. This can help teams introduce security analysis while evaluating their longer-term protection requirements.
Limitations
Shielding does not replace comprehensive security testing. It cannot independently correct insecure APIs, weak server-side authorisation or every application logic vulnerability.
Best use case: Commercial application developers that need to protect intellectual property and increase resistance to reverse engineering.
3. Zimperium – Best for Runtime Protection and Mobile Threat Defence
Zimperium combines mobile application protection with mobile threat defence capabilities. The supplied research identifies zShield for binary hardening and zDefend for in-app runtime application self-protection.
Runtime protection can be useful when an application runs on a device affected by malware, unauthorised instrumentation or operating-system compromise.
Depending on the selected configuration, these technologies can help identify suspicious execution environments and respond to certain threats.

Key features
- Application shielding.
- Runtime application self-protection.
- Mobile threat defence integration.
- Detection of selected hostile device conditions.
- Threat intelligence and security context.
Advantages
The combination of runtime defence and threat context can complement pre-release vulnerability testing. It is relevant to organisations that must consider attacks occurring after an application has been installed.
Limitations
The supplied research lists pricing as quotation-based. Buyers should verify the capabilities, platform coverage and response mechanisms included in the proposed deployment.
Best use case: Organisations seeking mobile runtime protection alongside a broader mobile threat defence programme.
4. Data Theorem – Best for Continuous Mobile and API Security
Data Theorem focuses on security risks involving both mobile applications and the backend services they communicate with.
A mobile client may appear secure while interacting with an API that exposes sensitive information, lacks appropriate access controls or contains overlooked endpoints.
The supplied research highlights mobile application analysis, API security, SDK analysis and backend visibility.
By assessing connected services alongside the mobile application, teams can better understand risks across the complete application environment.

Key features
- Mobile application security analysis.
- API security capabilities.
- SDK analysis.
- Backend service visibility.
- Identification of potential data exposure and overlooked endpoints.
Advantages
Its mobile-and-API perspective can help organisations investigate attack paths that cross application and backend boundaries.
Limitations
Pricing is listed as quotation-based in the supplied research. Teams should verify API discovery coverage, testing depth and integration requirements before purchasing.
Best use case: Organisations operating mobile applications that rely on multiple APIs and backend services.
5. Appdome – Best for No-Code Mobile Defence Integration
Appdome focuses on automating the integration of selected mobile application protections into application builds.
The supplied research identifies application shielding, anti-fraud controls and mobile threat defence capabilities. Its approach aims to reduce the need for extensive manual SDK integration.
This can help organisations incorporate security controls into established release processes, particularly when applications are updated frequently.

Key features
- No-code security integration.
- Build-time application protection.
- Anti-fraud capabilities.
- Mobile threat defence features.
- CI/CD workflow integration.
Advantages
Automation can reduce manual integration work and help standardise selected protection measures across application builds.
Limitations
The effectiveness of a deployment depends on the chosen controls, configuration and application architecture. Compatibility, performance and user experience should be evaluated before production use.
Best use case: Development organisations seeking to automate the addition of application protections to regular builds.
6. Promon – Best for Banking and Payment Application Protection
Promon SHIELD focuses on protecting applications running in potentially hostile environments. This is particularly relevant to banking, payment and other applications that handle sensitive transactions.
The supplied research highlights runtime shielding, anti-hooking, secure keyboard capabilities and SDK-based delivery.
Such protections can help resist selected attempts to inspect or manipulate application behaviour on compromised devices.

Key features
- Runtime application shielding.
- Anti-hooking protections.
- Secure keyboard capabilities.
- Protection for sensitive application workflows.
- SDK-based integration.
Advantages
Its emphasis on runtime protection makes Promon relevant to applications where fraud prevention and the integrity of sensitive transactions are important.
Limitations
Promon addresses the application protection side of security. Organisations still need secure backend development, vulnerability testing and appropriate monitoring.
Best use case: Financial services and developers protecting mobile payment and authentication workflows.
7. Veracode – Best for Enterprise Security Governance
Veracode provides application security capabilities within a broader enterprise security programme.
The supplied research describes its mobile offering as part of a governance-oriented platform that supports policy management, reporting and compliance workflows.
This can help organisations manage mobile application risks alongside security issues affecting other software projects.

Key features
- Mobile application security assessment.
- Static analysis capabilities.
- Policy-oriented reporting.
- Unified application security workflows.
- Support for enterprise governance processes.
Advantages
Centralised reporting can help security teams manage findings consistently across development teams and application portfolios.
Limitations
Organisations with specialised mobile requirements should verify the depth of binary analysis, runtime testing and mobile-specific protection capabilities included in their selected package.
Best use case: Enterprises that prioritise security governance and unified application risk reporting.
8. Checkmarx – Best for Mobile Source Code Analysis
Checkmarx supports static application security testing within a broader application security platform.
The supplied research highlights analysis of mobile source code written in Kotlin, Swift, Objective-C and Java. Static analysis can help developers identify insecure coding patterns before an application is compiled and released.
Managing mobile findings alongside other application security risks may also improve triage and remediation workflows.

Key features
- Mobile source-code analysis.
- Support for major Android and iOS development languages.
- Developer-oriented security findings.
- Integration with wider application security workflows.
- Correlation of code and dependency risks.
Advantages
Checkmarx can be useful for organisations seeking consistent source-code security processes across mobile and other software projects.
Limitations
Source-code analysis alone does not fully address runtime behaviour, binary tampering or vulnerabilities in backend services.
Best use case: Development teams seeking to manage mobile code security within an established application security platform.
9. Black Duck – Best for Dependency and Open-Source Security
Black Duck combines application security analysis with software composition analysis (SCA).
Mobile applications often depend on third-party SDKs, open-source packages and external libraries. These components can introduce vulnerabilities or licensing obligations that developers must manage.
The supplied research highlights static analysis, dependency auditing and open-source licence compliance.

Key features
- Static application security testing.
- Software composition analysis.
- Third-party dependency assessment.
- Open-source licence compliance.
- Platform-level security reporting.
Advantages
Dependency analysis helps teams identify potentially vulnerable components that may not be apparent from examining their own application code alone.
Limitations
Dependency and source-code analysis do not replace runtime testing or application shielding. Additional mobile-specific assessments may be required.
Best use case: Enterprises managing mobile applications with substantial open-source dependencies and complex software supply chains.
10. OWASP MobSF – Best Free Open-Source Mobile Security Analyzer
The Mobile Security Framework (MobSF) is an open-source tool for analysing mobile application packages.
The supplied research identifies support for static and dynamic analysis of formats including APK, IPA and APEX. It is particularly useful for cybersecurity students, penetration testers, researchers and teams that need an accessible starting point for mobile security assessment.

Key features
- Static analysis of mobile application packages.
- Dynamic analysis capabilities.
- APK and IPA analysis.
- API-related assessment capabilities.
- Potential integration into testing workflows.
Advantages
MobSF is free as an open-source project and offers a practical way to begin examining mobile applications without purchasing a commercial platform.
It can also support educational exercises and initial security reviews.
Limitations
Users are responsible for operating the tool, interpreting its findings and maintaining the deployment. It does not provide the same vendor support, service commitments or specialised shielding as some commercial products.
Self-hosted installations must be maintained securely and monitored for relevant vulnerabilities.
Best use case: Cybersecurity students, researchers, independent testers and organisations establishing a basic mobile application security testing capability.
6. Detailed Comparison Table
| Tool | Primary purpose | Main strength | Pricing in supplied research |
|---|---|---|---|
| NowSecure | Automated mobile testing | Testing and standards mapping | Tiered or quotation |
| Guardsquare | Application shielding | Binary protection and AppSweep | Tiered; free scanning option |
| Zimperium | Runtime protection | Runtime defence and threat context | Quotation |
| Data Theorem | Mobile and API security | Application/backend visibility | Quotation |
| Appdome | Mobile protection integration | No-code build-time controls | Tiered or quotation |
| Promon | Runtime application protection | Shielding for sensitive applications | Quotation |
| Veracode | Enterprise application security | Governance and reporting | Quotation |
| Checkmarx | Source-code analysis | Mobile SAST workflows | Quotation |
| Black Duck | Code and dependency security | SAST, SCA and licence analysis | Quotation |
| OWASP MobSF | Mobile application analysis | Free static and dynamic analysis | Free, open-source project |
Product capabilities, pricing and licensing can change. Verify current details directly with each provider.
7. Mobile App Testing vs Application Shielding
One of the most important findings from this comparison is that testing and shielding solve different problems.
Mobile application security testing
Testing identifies weaknesses in source code, application packages, runtime behaviour, dependencies and APIs. Its primary purpose is to discover vulnerabilities so developers can investigate and fix them.
Application shielding
Shielding helps resist selected attacks against applications after deployment. Depending on the technology, it can make reverse engineering, tampering and instrumentation more difficult.
For example, a mobile banking application might pass a source-code review but still face attempts to manipulate its runtime environment. Testing helps uncover software weaknesses, while shielding adds protection against selected attacks on the deployed application.
Neither approach guarantees security. Strong authentication, server-side access controls, secure data handling and ongoing monitoring remain essential.
8. How to Choose the Right Tool
Selecting a tool should begin with the application’s threat model, technical architecture and security requirements.
For beginners and students
Start with OWASP MobSF to learn how mobile application packages can be analysed. Use intentionally vulnerable applications or systems you are authorised to assess.
For mobile development teams
Evaluate automated testing solutions such as NowSecure and mobile/API assessment capabilities such as those described for Data Theorem. Prioritise integration with your development pipeline and a clear remediation process.
For banking and financial applications
Consider both testing and shielding. Guardsquare, Zimperium, Appdome and Promon address different aspects of application protection, while a testing platform helps identify underlying software weaknesses.
For enterprise security programmes
Evaluate Veracode, Checkmarx and Black Duck in the context of existing governance, source-code analysis and dependency-management workflows. Confirm that their mobile-specific capabilities meet your actual requirements.
For organisations with limited budgets
Begin with open-source analysis using MobSF and consider free scanning options such as AppSweep. Use the initial results to identify security gaps and determine whether additional commercial capabilities are justified.
9. Best Practices for Mobile Application Security
Choosing a tool is only one part of an effective mobile security programme. Organisations should establish repeatable processes for testing, remediation and ongoing maintenance.
- Define security requirements: Identify sensitive information, critical functionality and likely attack scenarios.
- Use a recognised framework: Structure requirements and assessments around OWASP MASVS where appropriate.
- Test throughout development: Integrate security checks into CI/CD instead of relying solely on a final review.
- Review APIs and dependencies: Assess the backend services and third-party components used by the application.
- Protect sensitive data: Avoid exposing secrets in source code or storing sensitive information insecurely.
- Evaluate shielding requirements: Determine whether the application’s risk profile justifies additional runtime protections.
- Validate findings: Investigate alerts, check for false positives and confirm that remediation addresses the underlying issue.
- Maintain security tools: Update scanners and self-hosted platforms, review relevant advisories and protect test environments.
- Retest after changes: Significant application updates and dependency changes can introduce new security risks.
- Document results: Maintain assessment records, remediation decisions and evidence of security testing.
These practices help make mobile security a continuous engineering activity rather than a one-time release requirement.
10. Frequently Asked Questions
What is the best mobile application security testing tool in 2026?
NowSecure ranks first in the supplied research, with a score of 9.0/10 for automated mobile application security testing. Guardsquare ranks second for shielding, and Zimperium ranks third for runtime protection and threat context. The most suitable tool depends on an organisation’s requirements.
Is OWASP MobSF enough for commercial applications?
MobSF provides a useful open-source starting point for static and dynamic analysis. Larger or higher-risk programmes may also require physical-device testing, formal reporting, vendor support, remediation workflows and application shielding.
Should mobile applications use both testing and shielding?
Applications that handle sensitive data or face elevated fraud risks may benefit from both. Testing helps identify vulnerabilities, while shielding helps resist selected attacks against deployed applications.
What is OWASP MASVS?
OWASP MASVS is a mobile application security verification standard that helps teams define and assess security requirements. It supports structured assessments but does not automatically certify an application as secure.
Are free mobile security tools reliable?
Free tools can provide valuable capabilities for learning, research and initial assessments. Their suitability for production depends on the required testing depth, support arrangements, operational capacity and the application’s risk.
How often should mobile applications be tested?
Testing should occur throughout development, before important releases and after significant changes. The appropriate frequency depends on release schedules, risk levels, dependency changes and organisational requirements.
Can static analysis identify every mobile vulnerability?
No. Static analysis can identify many code-level weaknesses, but it cannot reliably detect every runtime, backend, configuration or business-logic problem. Combining testing methods provides broader coverage.
11. Conclusion
Mobile application security in 2026 requires a layered approach that addresses vulnerabilities in code, APIs, dependencies and runtime environments.
The supplied research identifies NowSecure as its leading automated testing solution, Guardsquare as a specialist in application shielding, Zimperium as a runtime protection option and OWASP MobSF as a free starting point. Other tools provide capabilities for API security, no-code protection, enterprise governance and dependency analysis.
Rather than selecting a product based on its ranking alone, organisations should define their threat model, establish a repeatable testing process and add complementary protections where the risk justifies them.
CyberExy recommendation: Begin by assessing your application against relevant OWASP MASVS requirements. Integrate security testing into development, fix identified vulnerabilities and evaluate application shielding according to your application’s exposure and business requirements.