Node2Shell Vulnerability: Node.js CVE-2026-111497 Explained

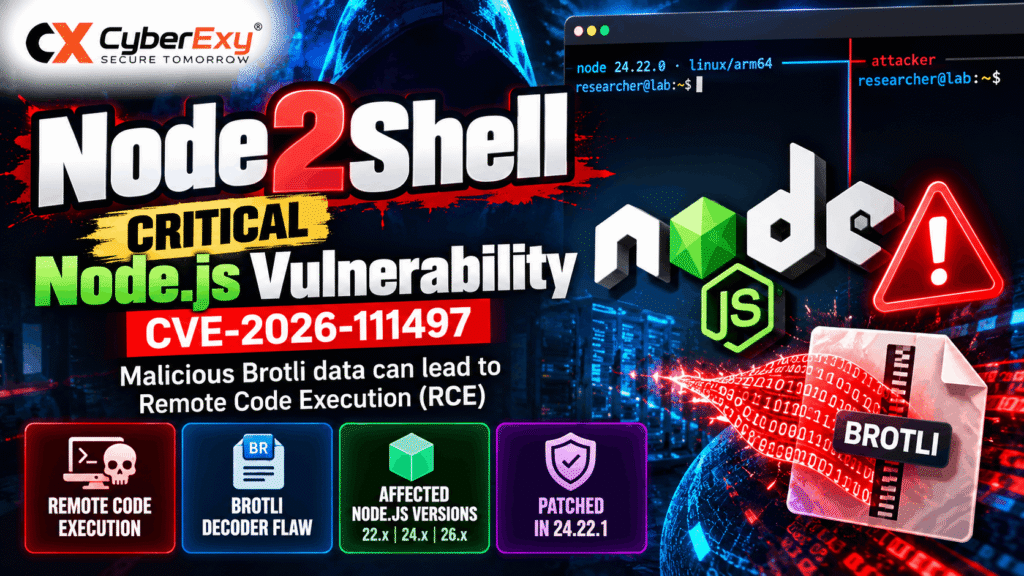
Node2Shell: Critical Node.js Brotli Vulnerability Could Enable Remote Code Execution
Published: October 23, 2026
A newly disclosed Node.js security vulnerability, tracked as CVE-2026-111497, has raised concerns about applications that process Brotli-compressed data. Security researchers at Imperva demonstrated how specially crafted compressed input could trigger a memory-safety flaw in an official Node.js build, potentially allowing remote code execution under certain conditions.
The vulnerability, referred to as Node2Shell, highlights the importance of keeping server-side JavaScript runtimes updated and reviewing how applications handle untrusted data.
What Is the Node2Shell Vulnerability?
According to Imperva Threat Research, CVE-2026-111497 involves an out-of-bounds write in the Brotli decoder bundled with Node.js. An out-of-bounds write occurs when software attempts to write data beyond an intended memory boundary. Depending on the circumstances, this type of memory corruption can affect application stability and potentially create opportunities for code execution.
Imperva reported reproducing the issue on an official Node.js 24.22.0 Linux ARM64 build without relying on a custom-compiled runtime or an instrumented debugging build. The researchers also reported that the same test input was rejected by Node.js 24.22.1, the patched release.
Successful exploitation is not guaranteed in every environment. The practical risk depends on the runtime version, application architecture, and whether attacker-controlled compressed data reaches the vulnerable decoding functionality.

How Can Applications Be Exposed?
Brotli is a compression algorithm commonly used to reduce the size of web responses and improve data-transfer efficiency. Node.js applications may encounter Brotli data through different processing paths.
One potential path involves the built-in fetch() API when an application retrieves compressed responses from an external service. Another may involve applications that use middleware to decode compressed incoming HTTP request bodies.
Imperva’s research discusses Express 5 and body-parser 2 configurations as relevant examples. However, exposure is configuration-dependent: a basic Node.js HTTP server does not automatically decompress every incoming Brotli request body.
Organisations should therefore investigate how their applications process compressed content instead of assuming that every Node.js deployment is equally vulnerable.
Which Node.js Versions Are Affected?
The Node.js security release published on October 21, 2026, identifies fixes for the affected release lines.
- Node.js 22.x: Update to 22.23.4 or a later supported security release.
- Node.js 24.x: Update to 24.22.1 or a later supported security release.
- Node.js 26.x: Update to 26.12.1 or a later supported security release.
Administrators should consult the official Node.js security advisory to confirm the appropriate version for their deployment and update to the latest supported release.

How Can Organisations Reduce the Risk?
Security teams should prioritise the following defensive measures:
- Update Node.js: Deploy a fixed version across production servers, development systems, containers, and build environments.
- Inventory deployments: Identify applications and container images running affected Node.js versions, including older images that may still be deployed.
- Review Brotli processing: Determine whether applications decode untrusted compressed responses or request bodies.
- Check dependencies: Review middleware and framework configurations that process compressed HTTP content.
- Apply temporary controls: Where immediate patching is not possible, consider restricting untrusted Brotli input through carefully tested application or network controls.
- Monitor security events: Review unusual application crashes, unexpected process behaviour, and relevant server logs.
Web application firewall rules may provide an additional layer of protection for some inbound traffic, but they are not a replacement for updating the vulnerable runtime.
Final Thoughts
Node2Shell demonstrates how a flaw in a widely used runtime component can affect applications that process compressed data. Although exposure depends on application configuration, organisations running affected Node.js versions should treat the advisory seriously.
The recommended priority is to upgrade to a fixed Node.js release, review Brotli-related data flows, and verify that all deployed environments are patched.
Official Sources
- Node.js, October 2026 Security Releases: https://nodejs.org/en/blog/vulnerability/october-2026-security-releases
- Imperva Threat Research, Node2Shell: From Brotli Data to Remote Code Execution: https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/