Rhysida Ransomware Claims 2.6TB Maryland Government Data

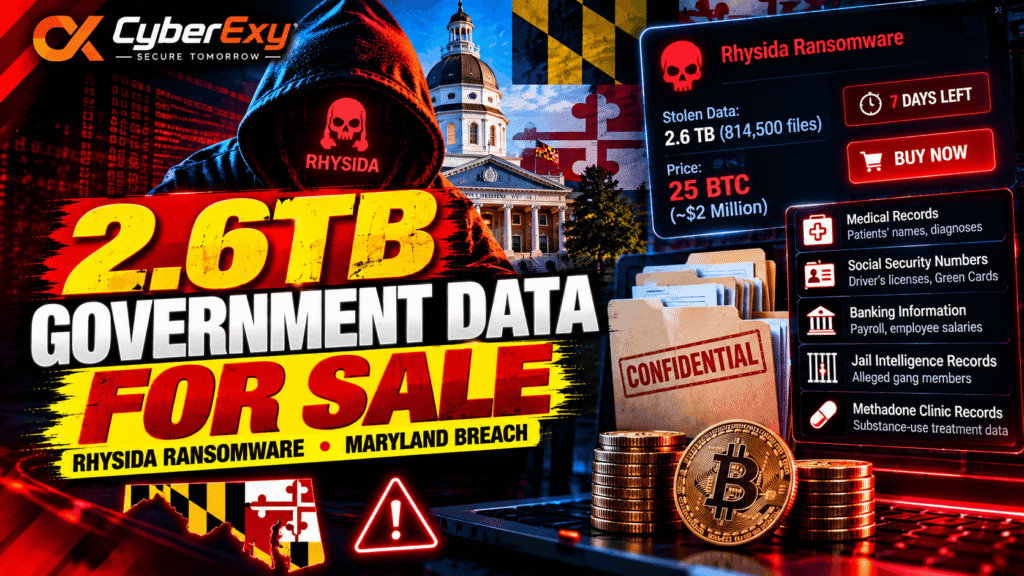
Rhysida Ransomware Gang Puts 2.6TB of Allegedly Stolen Maryland Government Data Up for Sale
Meta description: The Rhysida ransomware gang claims to have stolen 2.6TB of Anne Arundel County government data, allegedly including medical records, financial details and employee information.
Maryland County Confirms Cyberattack and Data Theft
Anne Arundel County, Maryland, has confirmed that an unauthorised actor accessed some of its government systems and copied files during a cyberattack discovered on August 28, 2026. The Rhysida ransomware gang has claimed responsibility and is advertising approximately 2.6 terabytes of allegedly stolen data for sale on its dark web leak site.
According to reporting by Recorded Future News, county officials launched an investigation after identifying suspicious network activity. The county confirmed that a limited number of systems were affected but has not publicly confirmed the full contents of the stolen files.
Rhysida claims the dataset contains approximately 814,500 files. The group is reportedly demanding 25 Bitcoin (BTC), described in the supplied report as worth approximately $2 million. It has also threatened to publish the information if its ransom demand is not met.
These figures and claims originate from the ransomware group and have not been independently confirmed by the county.
What Information Was Allegedly Stolen?
The threat actors claim the dataset contains highly sensitive personal, medical and government information, including:
- Medical faxes containing patients’ names and diagnoses.
- Social Security numbers, driver’s licences and immigration documents.
- Banking information and employee payroll records.
- Salary, pension and disciplinary information.
- Jail intelligence records.
- Records associated with methadone treatment services.
If verified, the exposure could create serious privacy and security risks for residents, county employees and individuals whose information appears in government records.
Medical and substance-use treatment information is particularly sensitive because its disclosure could affect individuals’ privacy and expose them to fraud or other forms of abuse.
However, the county is still investigating the copied files. The exact categories of affected information and the number of people potentially impacted remain unclear.
How Ransomware Extortion Works
Rhysida is using a familiar double-extortion approach: claim to have stolen data, demand payment and threaten to release or sell the information.
Unlike attacks focused exclusively on encrypting systems, data-theft extortion can pressure victims even when they restore services from backups. Organisations may face additional risks involving identity theft, financial fraud, regulatory obligations and reputational damage.
Advertising stolen data does not independently establish that every claimed file is authentic or that all listed information was successfully obtained. Investigators must examine the available evidence to determine the actual scope of an incident.
A Separate Cybersecurity Incident in 2025
Anne Arundel County has also announced plans to notify people who may have been affected by a separate cyber incident that occurred between January 28 and February 22, 2025. According to the supplied report, notification letters were expected to begin distribution during the week of October 19, 2026.
County representatives stated that the August 2026 attack was a separate incident. The two events should therefore not be treated as one breach.
How Government Organisations Can Reduce Ransomware Risks
Government agencies and other organisations should implement layered security controls to reduce the likelihood and impact of data theft.
Recommended measures include multifactor authentication, least-privilege access, network segmentation, continuous monitoring and regular vulnerability management. Sensitive databases should be protected with encryption and strict access controls, while backups should be isolated from ordinary network access and tested regularly.
Organisations should also maintain an incident-response plan covering evidence preservation, forensic investigation, legal obligations and communication with affected individuals. If sensitive information is exposed, potentially affected people should receive clear guidance on protecting their identities and accounts.
Conclusion
The reported Anne Arundel County incident highlights the continuing risks posed by ransomware groups that use stolen information as leverage. Although Rhysida claims to possess 2.6TB of government data, the county’s investigation will be essential to establish what was accessed and who may have been affected.
For public-sector organisations, strong identity controls, restricted data access, reliable backups and effective incident response remain critical components of ransomware resilience.
Sources for further reading:
- The Record — Anne Arundel County confirms data breach
- Anne Arundel County — Cyber incident information
- Cybernews — Reported Rhysida claim involving Montréal-Nord
CyberExy — Secure Tomorrow. Follow us for cybersecurity news, threat intelligence and practical security guidance.